I'm looking for:
AI & Automation Services

Automate workflows, integrate systems, and unlock AI-driven efficiency.

Recently viewed

Penetration Testing and VAPT London

Penetration testing and VAPT for London businesses, using Burp Suite, Metasploit, Nmap and Kali Linux to expose real attack paths across web applications, APIs, networks and cloud infrastructure. OWASP Top 10 methodology and CVSS scoring produce remediation reports you can act on.

Penetration testing starts from £2,500. Every engagement is quoted at a fixed price after a scoping call.

  • Testing from £2,500
  • Draft report within 5 working days
  • Retest of critical and high findings

Benefits and fit

What should a penetration test help you decide?

Leave with evidence of which weaknesses can really be exploited, what to fix first and confirmation that fixes for critical and high findings have worked.

Real attack path exposure

Burp Suite, Metasploit and Kali Linux tools actively exploit vulnerabilities to prove which CVEs can be chained into a full compromise. This gives security teams an honest picture of risk rather than a theoretical scan list with unchecked severity ratings.

A prioritised remediation roadmap

Every finding receives a CVSS score and a step-by-step fix recommendation. Critical and high findings include proof-of-concept evidence so developers understand the precise change required.

Evidence-grade compliance reports

CVSS-scored findings and OWASP Top 10 mapped reports give compliance leads concrete evidence for UK GDPR Article 32, ISO 27001 Annex A and Cyber Essentials submissions.

Retest verification included

Retesting critical and high findings after remediation confirms that fixes are effective before reports go to auditors or insurers. Verification reports document the before-and-after state for each finding.

Before you commit

Is VAPT the right starting point?

A good fit

You are an IT security manager, compliance lead or CTO at a London-regulated business and you need evidence-grade findings for UK GDPR Article 32 obligations, ISO 27001 audits or cyber insurance assessments.

A smaller change may be enough

If you only need weaknesses catalogued and ranked, a vulnerability assessment identifies them with automated scanning tools and scores each finding. A penetration test goes further and exploits them to determine real-world impact.

What we deliver

What your VAPT engagement covers

Expand a target type to see the tests and outputs. A scoping call confirms what is in scope before testing starts.

Web application penetration testing

Security teams get OWASP Top 10 web application tests using Burp Suite Professional and manual validation.

Authentication bypass, SQL injection, cross-site scripting, insecure direct object reference and broken access control findings are CVSS-scored and mapped to CWE references.

Retest verification confirms remediation before compliance submissions.

Network and infrastructure VAPT

IT managers get internal and external network assessments using Nmap, vulnerability scanners and Metasploit exploitation validation.

Open ports, unpatched services, misconfigured firewalls and lateral movement paths are documented with CVSS scores.

Findings map to ISO 27001 Annex A controls and NCSC Cyber Essentials requirements for straightforward compliance evidence.

REST API security testing

Development teams get REST API testing against OWASP API Security Top 10, covering broken object level authorisation, authentication failures, excessive data exposure and server-side request forgery.

Burp Suite intercept and custom scripts validate each endpoint. Findings include exploit code samples and precise developer fix instructions mapped to CWE identifiers.

Cloud penetration testing for AWS and Azure

Cloud engineering teams get AWS and Azure penetration testing covering IAM policy misconfigurations, S3 bucket exposure, network security group gaps, container security and serverless function vulnerabilities.

Findings follow NCSC cloud security guidance and map to ISO 27001 risk controls. Scoping calls confirm permission boundaries and rules of engagement before testing begins.

Vulnerability assessment and CVSS reporting

Compliance teams get automated and manual vulnerability assessments that score every finding against the Common Vulnerability Scoring System.

Reports include CVE references, asset risk ratings, board-ready executive summaries and a prioritised remediation plan.

Outputs satisfy UK GDPR Article 32 technical measures and support ISO 27001 Statement of Applicability updates.

Testing capabilities

Which tools and standards does the testing use?

Six technical capabilities sit behind every report.

Burp Suite Professional

Intercepting proxy, scanner and intruder modules test every web application request for injection, authentication and access control flaws.

CVSS scoring and CVE mapping

Every finding receives a CVSS v3.1 base score and a CVE or CWE reference so development teams prioritise fixes by verified risk severity.

OWASP Top 10 methodology

Web and API testing follows OWASP Top 10 and OWASP API Security Top 10, ensuring complete coverage of the most critical application risks.

Nmap and Metasploit exploitation

Network scanning with Nmap identifies open services. Metasploit validates exploitability, proving which vulnerabilities pose genuine compromise risk.

Cloud security testing

AWS and Azure assessments cover IAM, storage, networking and container security against NCSC cloud guidance and ISO 27001 risk controls.

Retest and verification reports

Post-remediation retests confirm critical and high findings are resolved. Verification reports provide before-and-after evidence for audit submissions.

Our process

From scoping call to a verified fix

Softomate maps scope, defines rules of engagement, executes controlled testing, scores findings against CVSS and delivers actionable remediation reports in short delivery phases. IT security contacts, compliance leads and technical owners stay involved from scoping through retest verification.

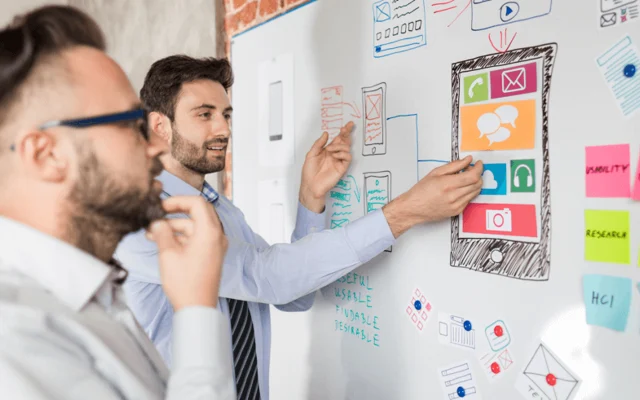
  1. Discover

    Scope the targets and rules

    Colleagues mapping a workflow with notes on a wall
    Library photography, not client work.

    Business context, compliance requirements and asset inventory are mapped in a scoping call with IT security managers, developers and compliance owners.

    What you receiveA target list, rules of engagement document and test schedule agreed before any active testing begins.

    How we do this

    For cloud work, the scoping call confirms service inventory, permission boundaries and rules of engagement before testing begins.

  2. Plan

    Agree methodology and criteria

    Reviewing charts and project information on a tablet
    Library photography, not client work.

    Testing methodology, OWASP Top 10 coverage depth, CVSS reporting thresholds and delivery timeline are agreed with IT and compliance stakeholders.

    What you receiveA signed rules of engagement document, test schedule and acceptance criteria aligned to UK GDPR, ISO 27001 or Cyber Essentials requirements.

    How we do this

    Scope, timeline and deliverables are agreed before any testing starts, so budgets stay predictable.

  3. Design

    Design the attack scenarios

    Working with source code at a desktop computer
    Library photography, not client work.

    Attack scenarios, test cases and tool configurations are designed for each target.

    What you receiveA test case inventory approved before active testing.

    How we do this

    Web application tests plan Burp Suite intercept flows. Network tests plan Nmap discovery sequences and Metasploit exploitation paths.

    Cloud tests plan IAM enumeration and privilege escalation checks.

  4. Build and integrate

    Test within agreed boundaries

    Colleagues reviewing software on two monitors
    Library photography, not client work.

    Active testing, exploitation and finding validation are executed within agreed scope boundaries.

    What you receiveEvidence screenshots, request logs and exploit proof-of-concept data for every finding.

    How we do this

    Burp Suite, Nmap, Metasploit and Kali Linux tools produce the evidence. Critical vulnerabilities trigger immediate client notification before the full report is drafted.

  5. Launch and optimise

    Report, debrief and retest

    A team attending a presentation in a meeting room
    Library photography, not client work.

    A draft report is delivered within five working days of testing completion, and a final report with a remediation plan follows after client review.

    What you receiveA CVSS-scored report, executive summary, remediation roadmap and retest verification of critical and high findings.

    How we do this

    A debrief call walks technical and compliance teams through priority findings. Retest verification confirms critical and high issues are resolved before audit submissions or insurance renewals.

Relevant results

What have comparable tests found and fixed?

Four outcomes from real Softomate VAPT engagements.

London FinTech lender · 85 staff

Critical findings remediated in three weeks

A London FinTech lender with 85 staff received a web application and REST API VAPT covering OWASP Top 10 and OWASP API Security Top 10. Fourteen critical and high findings, including broken object level authorisation and SQL injection, were identified with CVSS scores above 8.0.

The team remediated all critical issues within three weeks. Retest verification confirmed clearance before the FCA compliance submission.

14critical and high findings identified, with CVSS scores above 8.0

3 weeksto remediate all critical issues

NHS-contracted HealthTech platform · eleven GP sites

ISO 27001 audit passed after network VAPT

An NHS-contracted HealthTech platform covering eleven GP sites received a network infrastructure VAPT using Nmap and Metasploit. Nine high-severity findings including lateral movement paths and unpatched services were identified and mapped to ISO 27001 Annex A controls.

All high findings were remediated within four weeks. The team passed their ISO 27001 surveillance audit using the Softomate VAPT report as primary technical evidence.

9high-severity findings identified and mapped to ISO 27001 Annex A

4 weeksto remediate all high findings

London PropTech scale-up · AWS

AWS cloud VAPT cleared cyber insurance requirements

A London PropTech scale-up with AWS cloud infrastructure received a cloud penetration test covering IAM policies, S3 bucket configurations, network security groups and container security. Seven critical and high findings were identified and CVSS-scored. Remediation was completed within two sprints.

The cyber insurer accepted the Softomate retest verification report and renewed the policy without premium increase.

7critical and high findings identified and CVSS-scored

2 sprintsto complete remediation

London professional services firm · 120 staff

Cyber Essentials certification achieved in six weeks

A London professional services firm with 120 staff received a Cyber Essentials-scoped vulnerability assessment covering network perimeter, endpoint configurations and patch management. Twelve medium and high findings were identified and mapped to NCSC Cyber Essentials controls.

All findings were remediated and verified. The firm achieved Cyber Essentials certification six weeks after the initial assessment report.

12medium and high findings identified and mapped

6 weeksfrom the assessment report to Cyber Essentials certification

Case study outcomes from real Softomate VAPT engagements. Client names anonymised per NDA.

Delivery timeline

How long does a penetration test take?

Softomate agrees all timelines at the scoping stage. A draft report is delivered within five working days of testing completion, and a final report with a remediation plan follows after client review.

Web application test

3-5 working days

A standard web application penetration test.

Infrastructure VAPT

5-10 days

Typical for a mid-sized London network.

REST API testing

Adds 1-2 days

For complex integrations. Cloud testing on AWS or Azure varies by the number of services in scope.

Pricing

How much does penetration testing cost in London?

Penetration testing starts from £2,500.

Starting price for fixed-price quotations

Penetration testingFrom £2,500

The starting price, quoted at a fixed price after a scoping call.

What affects the price

Scope and environment
Penetration test pricing depends on scope size (number of URLs, IP ranges, user roles), environment complexity and time window. Scope, number of targets and OWASP Top 10 methodology depth affect the price.
What every quote includes
All pricing includes a written report with CVSS-scored findings, an executive summary and a step-by-step remediation roadmap. Retesting to verify fixes is included in the engagement fee.

We run a scope definition call with a senior tester before quoting. Fixed price follows the scope document, not a daily rate estimate.

Discuss your requirements →

Why Softomate

Why choose Softomate for vulnerability assessment and penetration testing?

Documented methodology, remediation advice written for your stack and a free retest.

Software development work shown on the Softomate homepage

Documented methodology

Every Softomate penetration test follows CREST-aligned methodology appropriate to the target scope.

Web application tests follow OWASP Testing Guide v4.2. Infrastructure tests follow PTES. API tests follow OWASP API Security Top 10.

Methodology is documented in the test plan, not implied.

Remediation guidance written for your stack

Every vulnerability finding includes a specific remediation recommendation written for your technology stack.

A finding in a Python/Django application gets different remediation guidance than the same finding in a Java/Spring application. Generic CVE links are not sufficient.

Every finding receives a CVSS v3.1 score, CVE or CWE reference, exploit evidence and a step-by-step fix instruction.

A free retest and evidence packages

Findings you have remediated are retested within 90 days of the original report at no additional cost.

Retest evidence is included in a supplementary report suitable for submission to Cyber Essentials Plus assessors, ISO 27001 auditors or FCA supervisory review.

Every penetration test is delivered with an evidence package formatted for the accreditation or regulatory submission you are targeting. Cyber Essentials Plus, ISO 27001 Annex A, FCA PS19/16 and NHS Digital DSP Toolkit evidence formats are all available.

FAQs

Questions before your penetration test

Further guidance

Explore the security testing detail

More on sector use cases, methodology and related security services. Open the areas relevant to your team.

VAPT use cases across London regulated industries

Penetration testing and VAPT engagements use Burp Suite, Nmap, Metasploit and Kali Linux to expose exploitable vulnerabilities across web applications, APIs, networks and cloud environments. The methodology suits compliance-heavy sectors where UK GDPR, ISO 27001 and FCA requirements demand evidence of regular security testing.

Web application testing for FinTech platforms

Burp Suite Professional tests FinTech web applications against OWASP Top 10 vulnerabilities including SQL injection, broken authentication and insecure direct object references. CVSS-scored findings map to FCA SYSC cyber rules and UK GDPR Article 32 obligations. Softomate clients typically reduce critical web application risk within four weeks of remediation completion.

Network VAPT for professional services

Nmap discovery and Metasploit exploitation validate open services, firewall gaps and lateral movement paths across professional services networks. Findings map to ISO 27001 Annex A controls and NCSC Cyber Essentials requirements. Softomate clients frequently achieve Cyber Essentials certification within eight weeks of implementing recommended fixes.

API security testing for SaaS and HealthTech

OWASP API Security Top 10 testing covers broken object level authorisation, excessive data exposure and authentication bypass in SaaS and HealthTech REST APIs. CWE-referenced findings give development teams precise fix instructions.

Cloud penetration testing for scale-ups

AWS and Azure penetration testing covers IAM misconfigurations, S3 bucket exposure, network security group gaps and container security vulnerabilities for growing London businesses. Findings follow NCSC cloud security guidance and map to ISO 27001 risk controls. Scoping calls confirm permission boundaries before testing begins.

Questions about retesting and reports
Is a retest included in the price?

Retesting to verify fixes is included in the engagement fee. Findings you have remediated are retested within 90 days of the original report at no additional cost, and the retest evidence is included in a supplementary report.

What clients say

"From understanding requirements and offering solutions, to implementing functionality accurately and very promptly, your business is in great hands."

R. Nagpal, Google review

"They have this attitude which says "Nothing is too much trouble." This is what makes them so approachable."

P. Mathur, Google review

Methodology, cloud and compliance detail

Cloud and API testing coverage

Cloud penetration testing for AWS and Azure covers IAM misconfigurations, storage exposure, network security groups and container security. REST API testing applies OWASP API Security Top 10 to authentication, authorisation and data exposure risks. Both outputs include CWE references for developer handover.

NCSC-aligned testing methodology

Testing methodology follows NCSC penetration testing guidance, OWASP Top 10 and PTES (Penetration Testing Execution Standard). Outputs map to ISO 27001 controls and UK GDPR technical measures, so security managers can satisfy multiple compliance frameworks from a single engagement without duplicate work.

OWASP and NCSC alignment

All testing follows OWASP Top 10, OWASP API Security Top 10 and NCSC penetration testing guidance, so findings map to compliance frameworks auditors and insurers recognise.

Compliance-ready evidence

Reports satisfy UK GDPR Article 32, ISO 27001 Annex A and Cyber Essentials requirements. Compliance teams receive one output that covers multiple frameworks without additional formatting work.

Related security and testing services

Endpoint protection services

Deploy CrowdStrike Falcon or Microsoft Defender for Endpoint to protect the devices that VAPT findings show are most exposed to compromise. See endpoint protection services.

Virtual CISO services

A virtual CISO translates VAPT findings into a board-level security programme, ISO 27001 governance plan and prioritised remediation roadmap your team can execute. See virtual CISO services.

Cyber security consultancy

Combine VAPT findings with ISO 27001 gap analysis, NCSC Cyber Essentials readiness and STRIDE threat modelling to build a complete security improvement programme. See cyber security consultancy.

Complete testing services

Extend VAPT coverage with functional, regression, performance and accessibility testing to give releases a complete quality and security sign-off. See complete testing services.

Work with us

Let's scope the systems you need tested

Tell us about your web applications, APIs, networks or cloud environments and any compliance deadlines. A scoping call confirms targets, permission boundaries and rules of engagement before any testing starts.

Deen Dayal Yadav, founder of Softomate Solutions

Deen Dayal Yadav

Online

Hi there 👋

How can I help you?