I'm looking for:
AI & Automation Services

Automate workflows, integrate systems, and unlock AI-driven efficiency.

Recently viewed

Cyber Security Consultancy London

ISO 27001 gap analysis, NCSC Cyber Essentials readiness, STRIDE threat modelling, security architecture review and ISO 27005 risk register development for regulated and growing London businesses.

IT directors, compliance managers and CTOs gain a structured evidence base for ICO, FCA SYSC and ISO 27001 audit requirements from a single engagement. Engagements produce prioritised remediation road maps that most clients execute within 90 days of delivery.

  • Quoted at a fixed price after a scoping call
  • Typically five to ten working days for a small or medium-sized business
  • Prioritised remediation road map

Benefits and fit

What should cyber security consultancy help you prove?

IT security managers, CTOs and compliance leads gain an evidence base for ICO, FCA and ISO 27001 audit requirements, with every recommendation tied to a specific framework control.

ISO 27001 gap analysis and roadmap

Gap assessments identify which Annex A controls are missing or insufficient against your current security baseline. A prioritised remediation road map and draft Statement of Applicability are produced, which compliance teams can execute internally or through Softomate implementation support.

NCSC Cyber Essentials readiness

Gap assessments cover all five technical controls: firewalls, secure configuration, user access control, malware protection and patch management. Each gap receives a specific remediation instruction. Most London businesses achieve Cyber Essentials certification within six to eight weeks of the initial gap assessment report.

Threat modelling for applications and architecture

STRIDE threat modelling identifies Spoofing, Tampering, Repudiation, Information Disclosure, Denial of Service and Elevation of Privilege risks in your application architecture and system design. Attack vectors and mitigations are mapped to OWASP Top 10 and ISO 27001 controls.

Risk register and UK GDPR evidence

Risk registers built on ISO 27005 methodology score every risk by likelihood and impact and map it to ISO 27001 Annex A controls. UK GDPR assessments cover Article 32 technical measures, DPIA requirements and ICO breach notification, with evidence formatted for ICO audit responses and ISO 27001 submissions.

Before you commit

Is cyber security consultancy the right starting point?

A good fit

You are a regulated or growing London business that needs a structured evidence base for ICO, FCA and ISO 27001 audit requirements, and a prioritised plan for what to fix first.

A technical test may come next

Consultancy is a strategic and governance service. Penetration testing actively exploits vulnerabilities to prove real-world attack paths, so many London businesses start with consultancy and then commission regular VAPT penetration testing. Ongoing leadership is available through virtual CISO services.

What we deliver

What does cyber security consultancy include?

Five areas of governance, architecture and risk work. Expand an area to see what it covers.

ISO 27001 gap analysis and implementation

Compliance teams get a structured ISO 27001 gap assessment covering all Annex A control domains. A prioritised remediation road map, draft Statement of Applicability and implementation guidance are produced.

Softomate can lead the full implementation programme or act as a technical adviser to your internal team. Most London clients achieve ISO 27001 readiness within six to twelve months of gap assessment completion.

NCSC Cyber Essentials readiness and certification

IT teams get a scoped Cyber Essentials gap assessment covering the five technical control domains with specific remediation instructions for each gap found.

Certification preparation includes self-assessment questionnaire support, evidence packaging and Cyber Essentials Plus technical verification coordination. Most Softomate clients achieve certification within six to eight weeks of gap assessment delivery.

STRIDE threat modelling and architecture review

Development teams get STRIDE threat modelling applied to web applications, APIs and cloud architecture. Attack vector identification, mitigation mapping to OWASP Top 10 and ISO 27001 controls, and security design recommendations give engineering leads a precise improvement list.

Reviews are used by NCSC-compliant development teams and as pre-launch security sign-off evidence for FCA technology assessments.

Security architecture reviews assess network segmentation, cloud configuration, identity management, API security controls and encryption practices, applying NCSC cloud security guidance, ISO 27001 controls and CIS Benchmarks. Design recommendations are ranked by risk impact.

Risk register and ISO 27005 assessment

Risk management leads get an ISO 27005-aligned risk register that scores every identified risk by likelihood and impact, maps risks to ISO 27001 Annex A controls and documents risk treatment decisions.

The register supports ISO 27001 audit evidence, FCA risk assessment submissions and board security reporting. Quarterly reviews update scores as systems and threat landscape change.

Security policy development and review

HR, legal and IT teams get a security policy suite covering information security, acceptable use, data classification, incident response and third-party access.

Policies are drafted or reviewed against ISO 27001 Annex A requirements, UK GDPR DPA 2018 obligations and NCSC guidance. Each policy includes an owner, review schedule and version control history to satisfy ISO 27001 document control requirements.

Scope

What shapes a cyber security engagement?

The frameworks that apply, your regulatory context and who delivers the road map.

Which frameworks apply

Engagements align to NCSC Cyber Essentials, ISO 27001:2022, UK GDPR and DPA 2018. The NIST Cybersecurity Framework is incorporated for organisations with US clients or global supply chain obligations. Every recommendation references the specific framework control, so your team knows which standard each change satisfies.

Regulatory context

Scope depends on your regulatory obligations (FCA, CQC, NHS, GDPR), existing control framework maturity and incident history. FCA SYSC cyber resilience rules, ICO enforcement expectations and NHS DSPT requirements are incorporated into the findings.

Who delivers the road map

Run the remediation road map internally, ask Softomate to lead implementation or act as technical adviser, or commission technical workstreams including VAPT testing.

Our process

How does a cyber security consultancy engagement run?

Softomate maps your security posture, assesses compliance gaps, develops the risk register and delivers a prioritised remediation road map in structured delivery phases. IT managers, compliance leads, legal contacts and business owners stay involved throughout.

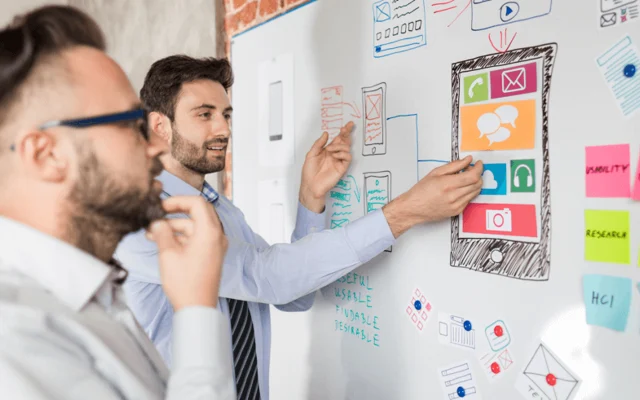
  1. Discover

    Map your context and controls

    Colleagues mapping a workflow with notes on a wall
    Library photography, not client work.

    Business context, compliance obligations, existing security controls and asset inventory are mapped in discovery interviews with IT managers, legal leads and business owners.

    What you receiveA security posture summary, compliance deadline list and scope document before the assessment methodology is confirmed.

    How we do this

    Scope depends on your regulatory obligations, control framework maturity and incident history. We assess these factors in a scoping session before committing to a fixed price.

  2. Plan

    Agree scope, schedule and criteria

    Reviewing charts and project information on a tablet
    Library photography, not client work.

    Assessment framework, workstream scope, timeline and deliverable format are agreed with IT, compliance and leadership stakeholders.

    What you receiveA signed engagement brief, assessment schedule and acceptance criteria aligned to ISO 27001, NCSC Cyber Essentials, UK GDPR and FCA SYSC requirements for your context.

    How we do this

    Scope, deliverables and timeline are agreed in writing before any assessment work begins, so budgets stay predictable.

  3. Design

    Design the assessment method

    Working with source code at a desktop computer
    Library photography, not client work.

    Assessment questionnaires, STRIDE threat model scope, ISO 27001 control review checklists and risk register templates are designed and approved before assessment work begins.

    What you receiveAn agreed assessment methodology document, so you know exactly which controls, systems and processes are in scope before the engagement starts.

  4. Build and integrate

    Assess, model and validate findings

    Colleagues reviewing software on two monitors
    Library photography, not client work.

    ISO 27001 gap assessment, STRIDE threat modelling, risk register development, UK GDPR compliance review and security policy analysis are completed with IT and compliance contacts.

    What you receiveA record-of-processing supplement, produced by an Article 32 measures review that maps findings to specific ICO guidance.

    How we do this

    Findings are validated with stakeholders during the assessment to ensure accuracy before the formal report is drafted. Every engagement includes a UK GDPR Article 32 technical and organisational measures review, completed concurrently.

  5. Launch and optimise

    Report, debrief and plan the fixes

    A team attending a presentation in a meeting room
    Library photography, not client work.

    The final assessment report, ISO 27001 gap analysis, risk register, remediation road map and compliance evidence are delivered within five working days of assessment completion.

    What you receiveA remediation roadmap prioritised by risk level, implementation complexity and regulatory deadline, with effort estimates so you can resource the work.

    How we do this

    A debrief session walks IT and leadership teams through priority findings. Softomate can remain engaged to implement the roadmap or commission technical workstreams including VAPT testing.

Relevant results

What have cyber security engagements achieved?

Four outcomes reported from Softomate cyber security consultancy projects. The figures belong to each project.

Financial services · London FinTech · 60 staff

London FinTech: ISO 27001 readiness achieved in six months

A London FinTech firm with 60 staff received an ISO 27001 gap analysis covering all Annex A control domains. A Statement of Applicability draft, risk register aligned to ISO 27005 and a prioritised remediation road map were produced within ten working days.

The firm implemented the road map internally within six months and achieved ISO 27001 certification at first audit attempt, supporting their FCA authorisation application process.

Ten working daysto produce the Statement of Applicability draft, risk register and road map

Six monthsto implement the road map internally and achieve ISO 27001 certification at first audit attempt

Case study outcomes from real Softomate cyber security consultancy projects. Client names anonymised per NDA. Results are specific to each project.

Legal services · London law firm · 110 staff

Law firm: Cyber Essentials certification achieved in seven weeks

A London law firm with 110 staff received an NCSC Cyber Essentials gap assessment covering all five technical control domains. Seventeen specific remediation instructions were produced, covering firewall rules, patch management gaps and user access control weaknesses.

The IT team remediated all findings within five weeks. Cyber Essentials certification was achieved seven weeks after the gap assessment report was delivered.

Seven weeksfrom the gap assessment report to Cyber Essentials certification

Seventeenspecific remediation instructions produced

Case study outcomes from real Softomate cyber security consultancy projects. Client names anonymised per NDA. Results are specific to each project.

Healthcare technology · NHS-contracted HealthTech platform

HealthTech platform: STRIDE modelling identified 11 pre-launch risks

An NHS-contracted HealthTech platform received STRIDE threat modelling applied to its web application and REST API before launch. Eleven attack vectors were identified, including broken object level authorisation and insecure session management.

All findings were mapped to OWASP Top 10 and ISO 27001 controls. Development teams remediated all critical findings within two sprints. The platform launched with a clean NCSC-aligned threat model as part of NHS DSPT submission evidence.

11attack vectors identified before launch

Two sprintsfor development teams to remediate all critical findings

Case study outcomes from real Softomate cyber security consultancy projects. Client names anonymised per NDA. Results are specific to each project.

SaaS · London scale-up

Scale-up: UK GDPR risk assessment resolved an ICO enquiry in six weeks

A London SaaS scale-up received an ICO enquiry regarding UK GDPR data processing records. A Softomate UK GDPR risk assessment produced Records of Processing Activities, DPIA outputs, lawful basis documentation and supplier DPA evidence within six working days.

The ICO enquiry was resolved without enforcement action six weeks after the assessment started. The risk register remains maintained quarterly as part of the ongoing compliance programme.

Six weeksto resolve the ICO enquiry without enforcement action

Six working daysto produce the Records of Processing Activities and supporting evidence

Case study outcomes from real Softomate cyber security consultancy projects. Client names anonymised per NDA. Results are specific to each project.

Delivery timeline

How long does a cyber security audit take?

A scoped cyber security audit for a small to medium-sized London business typically takes five to ten working days. Most Softomate clients receive their final assessment report within ten working days of engagement start. Timelines are agreed at the scoping stage with a detailed project plan before work commences.

Scoped audit

Five to ten working days

A small to medium-sized London business: discovery interviews, technical assessment, risk register development, reporting and a debrief session with IT and leadership teams.

Larger organisation or ISO 27001 readiness assessment

Three to six weeks

Larger organisations or those seeking ISO 27001 readiness assessments may require three to six weeks. Urgent regulatory deadlines are accommodated by prioritising the highest-risk workstreams in the first week.

Cyber Essentials certification

Six to eight weeks

Most London businesses achieve certification within six to eight weeks of the initial gap assessment. Cyber Essentials Plus requires additional technical verification and typically adds two to four weeks.

Planning information, not a delivery guarantee. Timelines are agreed at the scoping stage with a detailed project plan before work commences.

Pricing and running costs

How much does cyber security consultancy cost?

Cyber security consultancy in London typically ranges from £1,500 for a focused Cyber Essentials gap assessment to £15,000 or more for a full ISO 27001 gap analysis and remediation programme. All engagements are quoted at a fixed price after a scoping call.

Typical range in London£1,500 to £15,000 or more

From a focused Cyber Essentials gap assessment to a full ISO 27001 gap analysis and remediation programme. Quoted at a fixed price after a scoping call, with scope, deliverables and timeline agreed in writing before any assessment work begins.

What shapes the price

Scope factors
Organisation size, scope and the frameworks required. Scope also depends on your regulatory obligations (FCA, CQC, NHS, GDPR), existing control framework maturity and incident history.
Additional workstreams
FCA-regulated clients needing SYSC cyber resilience evidence or NHS organisations with DSPT obligations may require additional workstream scope.

Softomate provides fixed-price scoping calls so you receive a clear proposal before any work begins. Contact us to discuss your budget, compliance deadlines and risk priorities.

Discuss your requirements →
Why Softomate

Why choose Softomate for cyber security consultancy?

Multi-framework coverage, a fixed price and a road map you can resource, from a team that also delivers the technical work.

Software development work shown on the Softomate homepage

Multi-framework coverage in one engagement

Softomate assessments cover ISO 27001, NCSC Cyber Essentials, UK GDPR, NIST CSF and FCA SYSC rules in a single engagement. Clients receive one report that satisfies multiple compliance frameworks without duplicate assessment work.

We have completed ISO 27001 gap assessments, Cyber Essentials Plus readiness reviews and NIST CSF maturity assessments for UK financial services, professional services and technology firms. Reports include prioritised remediation roadmaps, not just finding lists.

UK obligations (ICO enforcement, NCSC guidance, Cyber Essentials scheme requirements) have specific UK-context interpretation. We work from that UK source guidance directly, rather than mapping your build onto a generic international security framework.

A fixed price and a road map you can resource

All cyber security consultancy engagements are quoted at fixed price after a scoping call. Scope, deliverables and timeline are agreed in writing before any assessment work begins so budgets stay predictable.

Every gap assessment is followed by a remediation roadmap that prioritises findings by risk level, implementation complexity and regulatory deadline. The roadmap includes effort estimates so you can resource the work, not just a list of things to fix.

Most Softomate clients achieve NCSC Cyber Essentials certification within six to eight weeks of gap assessment delivery. ISO 27001 readiness is typically achieved within six to twelve months of structured programme start.

Technical depth and connected delivery

STRIDE analysis applied to application architecture identifies attack vectors before deployment. Outputs map to OWASP Top 10 and ISO 27001 controls, giving engineering teams precise remediation guidance without security knowledge gaps.

FCA SYSC cyber resilience rules, ICO enforcement expectations and NHS DSPT requirements are incorporated into assessment findings so regulated London clients receive sector-specific guidance within the standard engagement.

Consultancy findings connect directly to VAPT engagements, endpoint protection deployments and virtual CISO programmes, so clients move from assessment to implementation without changing security partner.

FAQs

Questions about cyber security consultancy

Further guidance

Explore the cyber security consultancy details

Technical capabilities, sector use cases, related security services and client feedback. Open the areas relevant to your team.

Cyber security consultancy technical capabilities

ISO 27001 and ISO 27005 methodology

Gap assessments, Statements of Applicability and ISO 27005 risk registers are built to specification for certification auditors and FCA risk assessment submissions.

STRIDE threat modelling

STRIDE analysis applied to web applications, APIs and cloud architecture identifies attack vectors before deployment. Outputs map to OWASP Top 10 and ISO 27001 controls.

NCSC Cyber Essentials framework

Cyber Essentials and Cyber Essentials Plus gap assessments cover all five technical control domains with specific remediation instructions for each identified gap.

NIST Cybersecurity Framework

NIST CSF alignment is incorporated for organisations with US clients, global supply chain obligations or investor security due diligence requirements alongside UK frameworks.

UK GDPR and ICO compliance

UK GDPR Article 32 technical measures, DPIA assessments, Records of Processing Activities and ICO breach notification procedures are assessed and documented for audit use. FCA-regulated clients receive additional assessment of SYSC cyber resilience rules.

FCA SYSC cyber rules

FCA SYSC cyber resilience requirements are mapped to ISO 27001 controls and NCSC guidance for regulated firms requiring auditor-grade evidence of compliance.

Cyber security consultancy use cases across London sectors

Cyber security consultancy engagements use ISO 27001 gap analysis, NCSC Cyber Essentials assessment, STRIDE threat modelling and ISO 27005 risk register development to give London businesses a structured, evidence-grade security improvement programme. The approach suits regulated and growing businesses where ICO, FCA and ISO 27001 obligations make credible compliance evidence a commercial necessity. Most Softomate clients receive their final assessment report within ten working days of engagement start.

ISO 27001 gap analysis for FinTech businesses

FinTech businesses preparing for ISO 27001 certification or FCA authorisation receive a structured gap assessment covering Annex A control domains, Statement of Applicability draft and a prioritised remediation road map. FCA SYSC cyber resilience rules are embedded in the gap analysis. Softomate clients in financial services typically achieve ISO 27001 certification within nine months of gap assessment completion.

Cyber Essentials for London professional services

Law firms, accountancy practices and consultancies receive NCSC Cyber Essentials gap assessments covering all five technical control domains. Specific remediation instructions for each gap guide IT teams through certification preparation. Softomate clients typically achieve Cyber Essentials certification within six to eight weeks of gap assessment report delivery.

STRIDE threat modelling for SaaS platforms

SaaS and HealthTech development teams receive STRIDE threat modelling applied to web applications, REST APIs and cloud architecture before launch. Attack vectors map to OWASP Top 10 and ISO 27001 controls. Softomate clients use STRIDE outputs as pre-launch security sign-off evidence for FCA technology assessments and NHS DSPT submissions.

UK GDPR risk assessment for scale-ups

London scale-ups handling personal data receive UK GDPR compliance assessments covering Article 32 technical measures, DPIA requirements, Records of Processing Activities mapping and ICO breach notification procedures. DPA 2018 retention schedules and supplier DPAs are reviewed. Evidence produced satisfies ICO audit queries without additional reformatting or legal interpretation.

Related security services

Virtual CISO services

A virtual CISO translates cyber security consultancy findings into a board-level programme, ISO 27001 certification delivery and ongoing monthly governance without a full-time hire.

Penetration testing and VAPT

VAPT engagements provide the technical evidence that consultancy risk registers and ISO 27001 Statements of Applicability need to demonstrate real-world security control effectiveness.

Endpoint protection services

CrowdStrike Falcon and Microsoft Defender for Endpoint deployments implement the malware protection and device security controls identified in cyber security consultancy gap assessments.

Complete testing services

Functional, regression, performance and security testing provide quality and compliance evidence that feeds directly into ISO 27001 control evidence and consultancy risk assessments.

What clients say

"From understanding requirements and offering solutions, to implementing functionality accurately and very promptly, your business is in great hands."

R. Nagpal, Google review

"The team and Deen Dayal Yadav have always been very cooperative and will always do their very best in assisting with any requirements. They have this attitude which says 'Nothing is too much trouble.' This is what makes them so approachable."

P. Mathur, Google review

"It's not only about the quality but also the attitude with they try to understand the clients needs and accordingly customise the solutions. Their attention to detail is spectacular also."

S. Mohanty, Google review

Work with us

Let's talk about cyber security consultancy

Cyber security consultancy for ISO 27001 certification, NCSC Cyber Essentials and regulatory compliance. STRIDE threat modelling, ISO 27005 risk registers and UK GDPR assessments give your business evidence-grade security documentation accepted by auditors, regulators and insurers.

Deen Dayal Yadav, founder of Softomate Solutions

Deen Dayal Yadav

Online

Hi there 👋

How can I help you?